MOD-AUTH · Authentication
Sign-in your customers trust, on the identity stack you choose.
Passkeys, biometrics, one-time codes and social sign-in for customers; single sign-on for your staff. The module works with the identity providers enterprises already run, or brings its own.
- 14connectors
- 6platforms run it
- +1your own, too



- 01 · The job
Secure by default, quick every day.
Customers sign in with a passkey or Face ID, confirm payments with a second factor, and recover access without calling support. Sessions, devices and trusted browsers are managed per user, and staff sign in to the backoffice through your company's single sign-on.
- Passkeys and device biometrics
- One-time codes by app, SMS or email
- Strong customer authentication for payments (PSD2)
- Device binding and trusted devices
- Session management and remote sign-out
- Single sign-on for staff
- 02 · The connectors
Keycloak, Okta, Auth0, or plain OAuth.
The module speaks the standards, OAuth 2.0, OpenID Connect and SAML, so it sits behind the identity provider you already run. Social sign-in and second factors plug in the same way.
Identity providers
- Keycloak
- Okta
- Auth0
- Microsoft Entra ID
- AWS Cognito
- Firebase Authentication
- Ping Identity
Social sign-in
- Sign in with Apple
- Microsoft
Second factors
- Passkeys (WebAuthn)
- Authenticator apps (TOTP)
- Twilio Verify
- Push approval in your app
- 03 · Your own
Your identity provider stays in charge.
Any provider that speaks OpenID Connect or SAML connects without custom code. If you have none, the module's own authorization server is deployed with your platform and handed over with the rest of the source.
In-house, or a provider you already use- Any OpenID Connect or SAML provider
- Or a self-hosted authorization server
- Your password, lockout and session policies
In production
Running in these platforms.
 Crypto exchangeSpot trading, order book and custody wallets. Your exchange, live in a month.
 Stock exchangeEquities trading, portfolios and market data, under your brand.
 SoftPOSAny phone becomes a certified payment terminal. No hardware.
 Banking appAccounts, cards and transfers. A neobank under your brand.
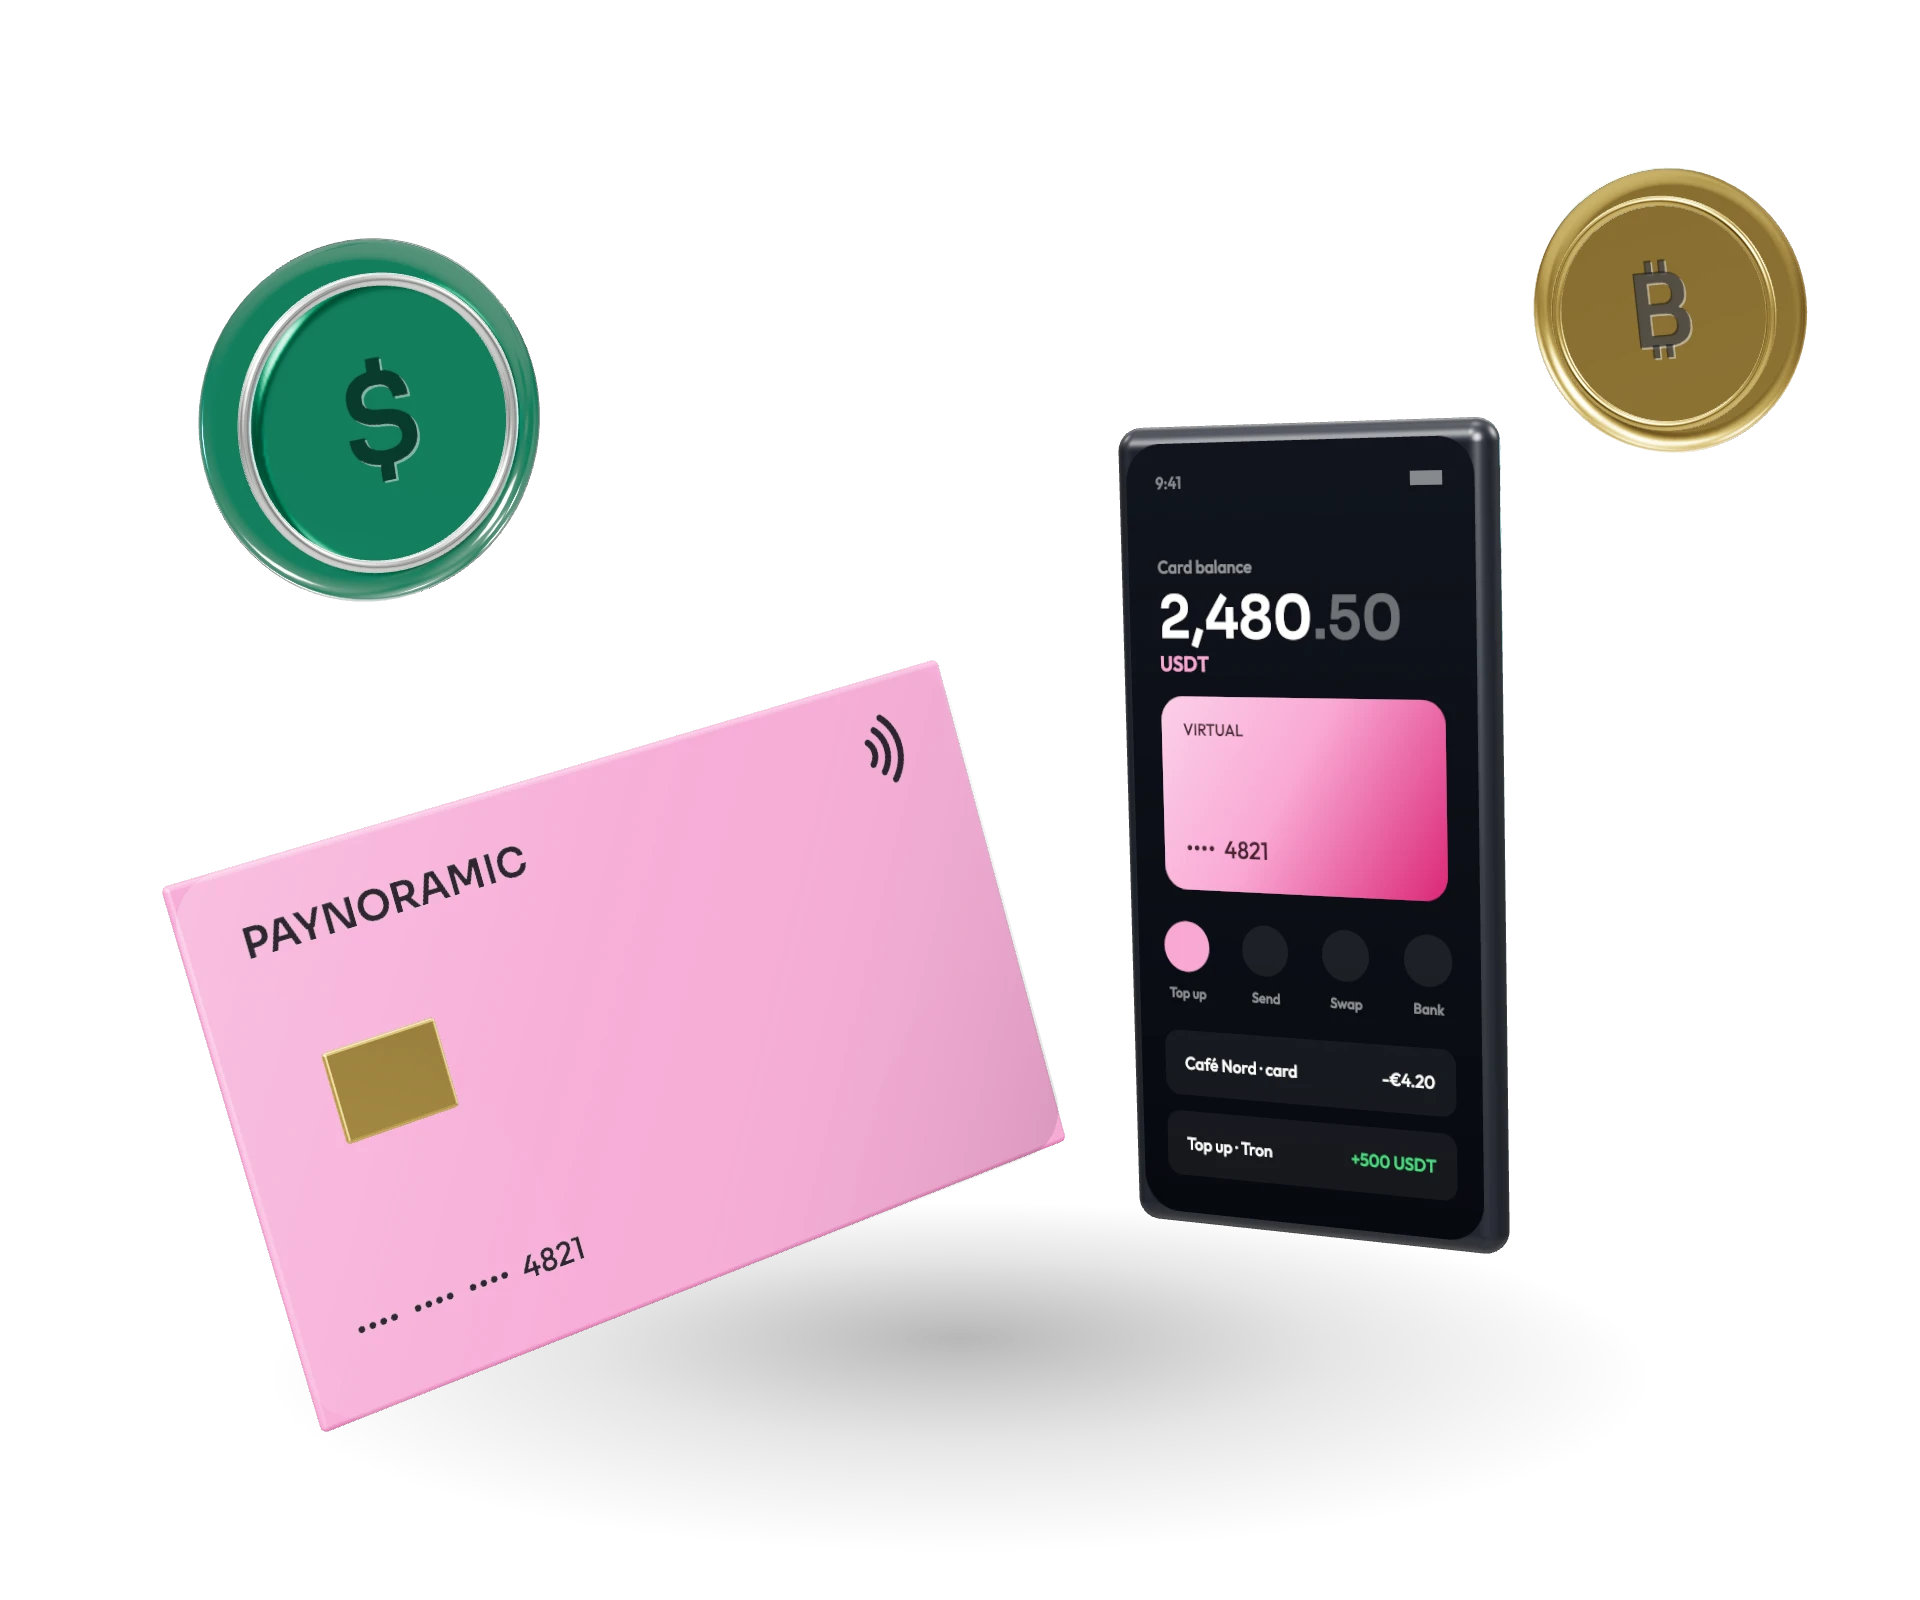 Crypto card appA stablecoin wallet with its own cards. Top up in crypto, pay anywhere, send money to any bank.
 Payment gatewayCheckout plus merchant dashboard, assembled for your flow.
Questions
Asked about this module.
Do customers need a password?
No. Passkeys and device biometrics can replace passwords entirely, with one-time codes as a fallback on devices that do not support them.
Can staff use our company login for the backoffice?
Yes. The backoffice signs staff in through your identity provider with single sign-on, and their roles can follow your directory groups.


Start your project
Tell us the idea. We'll show you the platform.
One call is enough to map your product to the modules that already exist.
- Response in under one business day
- NDA on request
- No obligation